
Coupang said it is pursuing follow-up security measures after last year’s personal data leak, including improving key management and monitoring systems and introducing an information security advisory committee made up of outside experts.
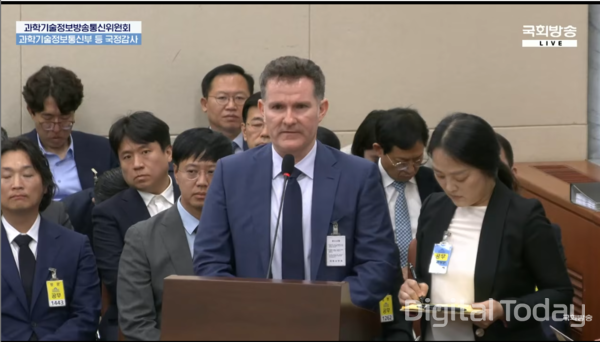
Brett Mathis (브렛 매티스), Coupang’s chief information security officer, appeared as a witness on Oct. 6 at a National Assembly Science, ICT, Broadcasting and Communications Committee audit of the Ministry of Science and ICT and outlined security improvements made after the leak.
Song Ki-heon (송기헌), chairman of the committee, said Mathis was called to confirm what follow-up measures Coupang is taking after the personal data leak.
Mathis said, "I once again express regret and apologize for the inconvenience caused to the public by the information breach incident." He said the company has worked to strengthen its information security system together with relevant government agencies, including the Ministry of Science and ICT.
He said the company has improved its key management policy, introduced a hardware-based key management system and strengthened its monitoring system.
He also said it continues to invest in information security, and cited the formation of an external information security advisory committee and the adoption of passkeys as follow-up measures.
Coupang last month launched an information security advisory committee involving 7 outside experts in information security, law, management and IT. It also introduced passkeys that use biometric information registered on devices, instead of passwords, for logins.
Coupang was investigated by the government after a large-scale personal data leak occurred in late November last year. The Ministry of Science and ICT and other agencies investigated Coupang’s security system and the circumstances of the incident, and Coupang has carried out improvement work on key management and its authentication and monitoring systems based on the investigation results.
 Seulgi Son
sageson@d-today.co.kr