
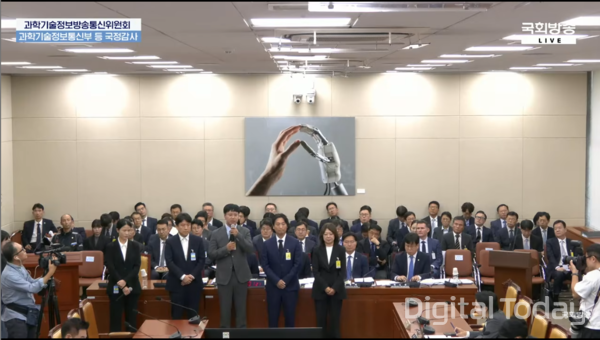
A series of hacking and personal data leak incidents across industries including telecoms, platforms, payments, healthcare and matchmaking put companies' lax security systems and post-incident responses under scrutiny at a parliamentary audit. Companies that attended the audit apologised and pledged to expand security investment, compensate 피해 and prevent recurrence.
Witnesses at an audit of the Ministry of Science and ICT by the National Assembly Science, ICT, Broadcasting and Communications Committee on Oct. 6 included officials from TVING, Toss Payments, Woowa Brothers (Baedal Minjok), Healing Paper (Gangnam Unni), Duo, LG Uplus and Coupang, which recently faced security breaches and personal data leak issues.
The types of incidents differed by company, but a common criticism was that there were gaps across security systems, including basic information security management, detection of abnormal signs and the process of preserving and submitting materials after incidents.
TVING faced concentrated criticism for storing developer access keys in plain text in source code and for failing to properly detect abnormal signs while a large volume of data was leaked. It was also criticised for insufficient fundamental system improvements after earlier penetration tests flagged hardcoding vulnerabilities, as it only improved individual projects.
Choi Ju-hee (최주희), head of TVING, said, "I clearly realised we were negligent about security." She said the company will expand information security staff and investment and build a zero-trust-based security system.
At Baedal Minjok, a case was raised in which a customer service agent unlawfully looked up a customer's address and front door passcode and handed the information to outsiders. Woowa Brothers explained it was an incident stemming from a disguised job applicant and said it increased management and oversight items for personal data processing contractors from 30 to more than 50.
Toss Payments also faced criticism that abnormal-sign monitoring did not operate in the process of a large outflow of payment-related information. The company said it is strengthening not only internal security systems but also management and oversight of merchants.
At healthcare and matchmaking platforms, the sensitivity of leaked information became an issue.
At Gangnam Unni, about 1 million cases of procedure-related information and counselling photo URLs were leaked, and at Duo it emerged that member information including reasons for not completing military service, names of ex-spouses, reasons for divorce, annual income, assets and health status was leaked externally.
Gangnam Unni said it will expand information security staff and investment and provide damages compensation and legal support for secondary 피해. Duo said it is difficult to prepare a uniform compensation plan due to the nature of its service, but said it will compensate if damage from the leaked information is confirmed.
LG Uplus again became controversial over the process of reinstalling the operating system of related servers after it was notified of signs of a security breach.
Han Jun-ho (한준호), a lawmaker from the Democratic Party, said LG Uplus carried out operating system work on the related servers on Aug. 12 after the Korea Internet & Security Agency (KISA) notified it of signs of a breach on July 19. He questioned the timing of preserving originals and creating forensic images.
LG Uplus said it submitted server images capable of forensic analysis to KISA and believes the images were also created after the KISA notification. Han said, "If the original was preserved and a forensic image was submitted, why did the joint public-private investigation team announce it could not confirm intrusion traces and attack paths due to operating system reinstallation and disposal?"
Deputy Prime Minister and Minister of Science and ICT Bae Kyung-hoon (배경훈) said, "We will have the ministry confirm it as well."
Coupang said it improved its key management policy, hardware-based key management system and monitoring system after a personal data leak incident last year. It also presented follow-up steps including forming an external information security advisory committee and adopting passkeys.
After incidents, companies' cooperation with investigations and their stance on submitting materials also became an issue.
Hwang Jung-a (황정아), a lawmaker from the Democratic Party, called for providing security consulting and AI support to companies that actively cooperate with investigations, while imposing strong sanctions on companies that conceal incidents or are uncooperative in submitting materials.
Bae said, "There is a need to respond strictly to companies trying to conceal security breaches, such as by insincerely submitting materials, failing to respond to breaches or refusing to submit materials."
The string of breaches is also expected to increase calls to strengthen basic security systems in advance, including management of access privileges and authentication information, detection of abnormal signs and preservation of originals, as well as compensation after incidents.
 Seulgi Son
sageson@d-today.co.kr