
Signs were raised at a parliamentary audit that an IP address used in a recent hacking attack targeting the financial sector also attempted to access internet-only banks from January. Concerns were also raised that financial companies review past access records over different periods, which could cause them to miss signs of intrusion. The argument was that the financial authorities should strengthen the scope and verification methods of emergency security inspections so they do not stop at a simple checklist review.
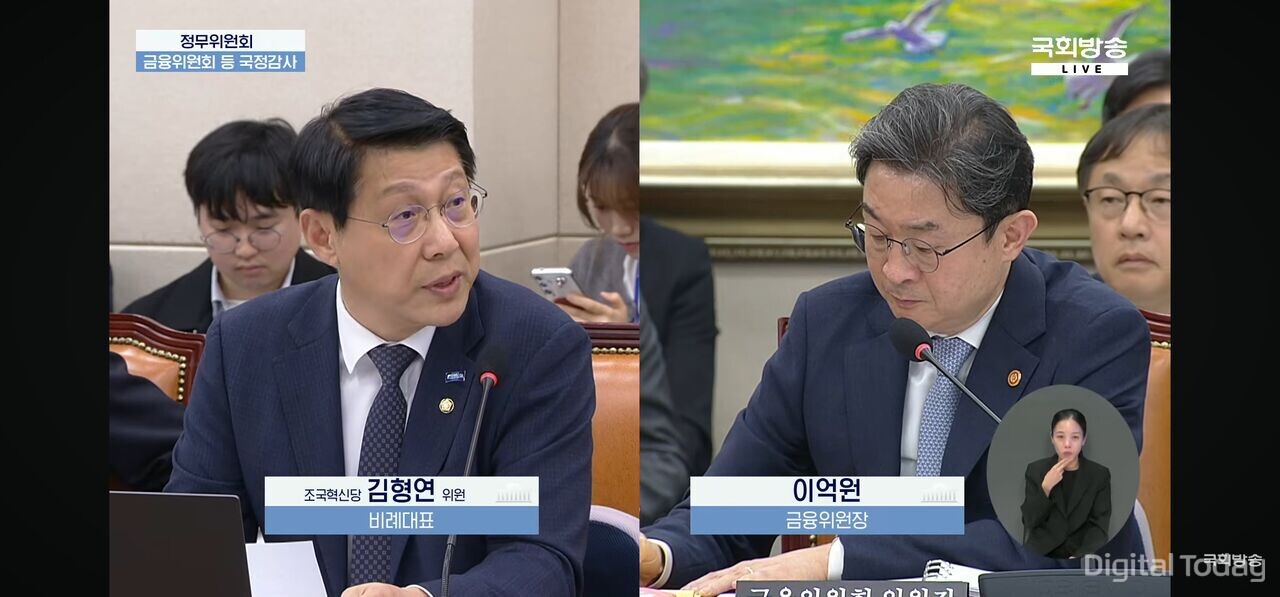
At an audit of the Financial Services Commission by the National Assembly Political Affairs Committee on Oct. 8, Kim Hyeong-yeon (김형연), a lawmaker from the Rebuilding Korea Party, cited an earlier remark by Financial Services Commission Chairman Lee Eok-won that “a single unmanaged gap can become a vulnerability in the entire security system.” Kim questioned the status of intrusion detection at financial companies and how the financial authorities conduct inspections.
According to Kim, the IP address used in the recent Shinhan Bank hacking had a record of accessing 2 internet-only banks on Jan. 24. Kim’s office checked 3 internet-only banks based on attack IP addresses shared by financial authorities and found traces of access at 2 banks on the same day. He said this could be confirmed because the banks reviewed one year of access records.
Kim said it was not possible to conclude the same IP belonged to the same person, but said the same IP that attacked Shinhan Bank accessed 2 firms in the same sector on the same day and a personal data leak occurred at Shinhan Bank 8 months later.
He added it could not be ruled out that the January activity was advance reconnaissance. He said security work requires preparing for the worst and that at least one year of records should be reviewed.
Kim criticised the effectiveness of the Financial Supervisory Service checklist, saying review periods differ by institution.
Kim pointed to the Financial Supervisory Service’s emergency security inspection checklist as a cause of differing review periods for intrusion incidents across financial firms.
He said the checklist distributed by the watchdog includes items such as whether firms checked for intrusion attempts and damage and whether they operate a real-time security monitoring system, but does not specify a concrete review period or verification standards.
Kim said a firm could answer “yes” whether it reviewed 3 months or 1 year. He said Shinhan Bank, where an incident occurred, could also answer “yes” on whether it operated monitoring because it ran monitored systems.
He particularly took issue with some banks reporting no anomalies after checking only the latest 3 months of records.
When Kim asked whether “no anomalies” after checking 3 months and “no anomalies” after checking 1 year were the same, Lee answered they were not.
Kim also asked whether financial authorities check not only checklist responses but also specific supporting evidence.
Lee said that after this incident, authorities first instructed a swift review of 12 items. He said financial companies should also conduct additional checks and that authorities would receive results, assess the overall situation and then conduct another inspection.
On submission of inspection results, Lee said some had been received from banks and that other sectors such as card companies were scheduled to submit additional results.
Kim urged authorities to have all financial companies recheck at least one year of records and to receive reports not just in “yes or no” form but including specific review periods and where findings were discovered.
Kim also pointed to insufficient incident detection capabilities at financial companies.
According to 자료 submitted by the Financial Supervisory Service to Kim, 91 cases of electronic financial incidents and intrusion incidents in the financial sector from 2022 through August this year were recognised only after more than a month had passed. Of those, 17 were identified only after more than a year.
The longest case took 902 days for an incident to be recognised. Most were internal IT incidents such as program errors, but cases were also confirmed in which detection was delayed for a long period even for external intrusion incidents, he said.
Criticism was raised that the latest string of hacking incidents in the financial sector also exposed limits in detection systems.
Kim said that in Hyundai Capital’s case, an intrusion occurred at dawn on Sept. 27 but the incident was recognised only on Oct. 2. He said access records of the related IP were confirmed during an investigation into hacking incidents at another financial company.
Kim also said that at Shinhan Bank, although the affected service was subject to security monitoring, the first to detect abnormal signs was not the security department but the development department.
Kim said if firms do not know about errors occurring internally and also do not know for months about intrusions from outside, responses will inevitably come only after incidents. He said the causes of delayed incident recognition and measures to improve them should be prepared.
He asked the Financial Services Commission to analyse the causes of delayed detection and improvement measures and report to his office before the comprehensive audit. He also requested 자료 on the results of an information security inspection conducted by the Financial Supervisory Service in September last year and the status of implementation of follow-up measures.
 Ji-young Lee
ljy@d-today.co.kr