
South Korea's financial authorities plan to raise security standards for digital asset operators to the level of financial companies. They plan to include obligations to ensure information technology (IT) safety and liability for damages in a digital asset law. They also plan to allow pre-emptive blocks on deposits and withdrawals even before the law takes effect if hacking is suspected.
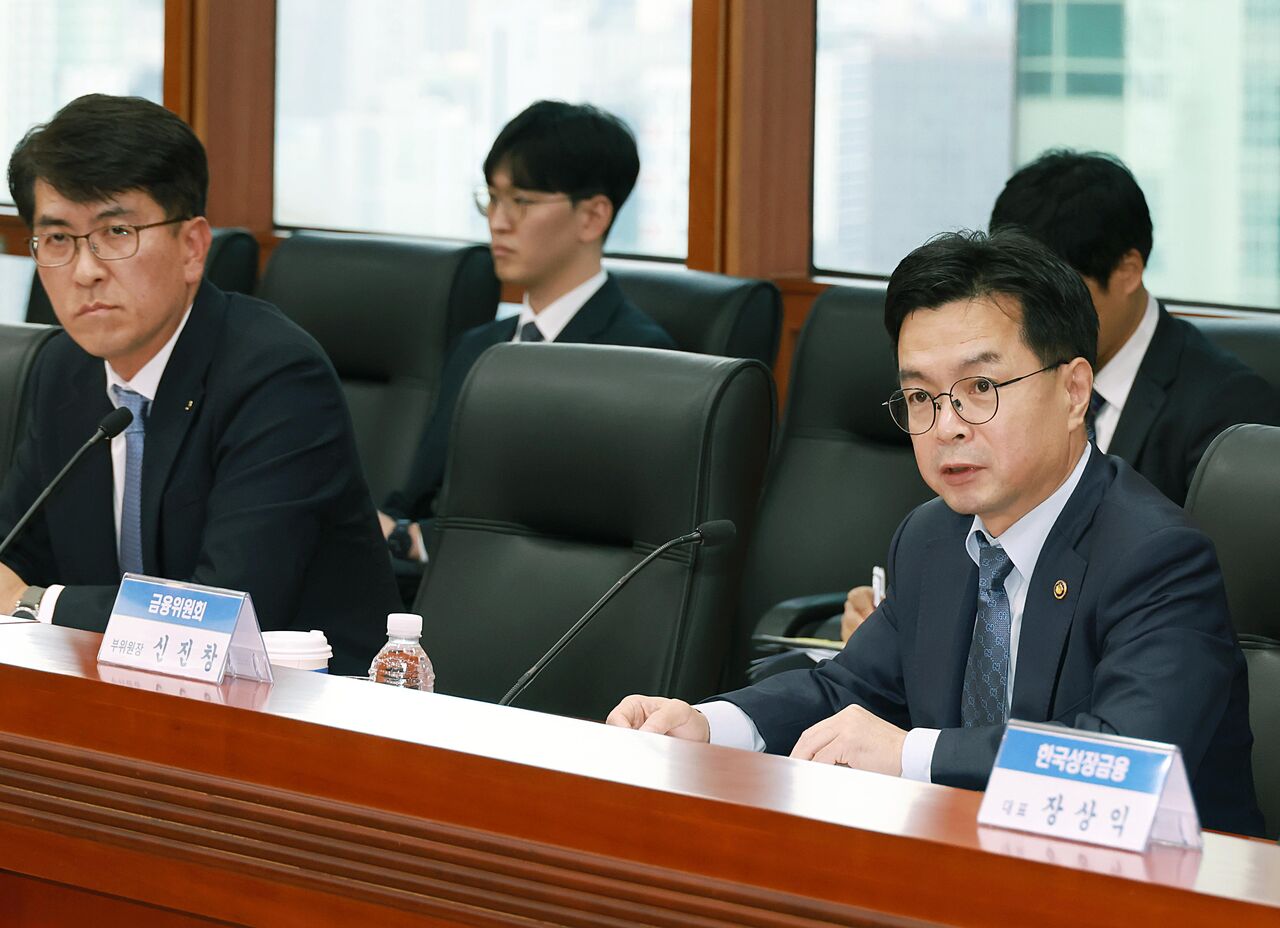
The Financial Services Commission held a "digital asset sector security measures meeting" chaired by Vice Chairman Shin Jin-chang (신진창) on Nov. 12 and discussed responses to a series of recent data leaks and security breaches at digital asset exchanges at home and abroad.
Shin pointed out that security awareness among some digital asset operators remains at a pre-institutional level, contrary to market growth and expectations for the industry.
He said digital asset operators should have security systems at the same level as traditional financial companies because they custody, store and manage users' assets. He called for a shift in security awareness.
The FSC plans to impose on digital asset operators IT safety obligations and liability for damages at the level of financial companies through the digital asset law now being prepared.
As legislation will take time, it decided to apply immediately implementable security measures even before the law is enacted, including 24-hour monitoring and incident reporting systems, a higher share of cold wallet storage and additional reserve accumulation.
It ordered exchanges to establish round-the-clock monitoring and response systems, reflecting the digital asset market's 24-hour operation.
If a security breach is suspected, such as abnormal large-scale transactions, responsible personnel must immediately implement control measures. Operators that find it difficult to run a 24-hour response system were told to process deposits and withdrawals only during hours when monitoring is possible and to notify users in advance.
It will also increase the share of users' assets stored in cold wallets.
Under current digital asset business supervision regulations, at least 80 percent of users' assets must be stored in cold wallets. The average cold wallet storage share among all operators is currently above 95 percent.
The FSC said there is also a need to review a plan to reduce user assets held in hot wallets to the minimum level needed for trading support and to spread them across multiple hot wallets. It also told operators to secure sufficient insurance payout limits and reserve holdings in preparation for hacking losses.
It will also extend IT safety standards applied to financial companies to digital asset operators.
Operators must have IT and information security personnel and facilities and establish technical, managerial and physical standards to ensure transaction safety. They also plan to require operators to analyze and assess vulnerabilities in information processing systems and information and communications networks and then carry out necessary remedial measures.
If a security breach or an abnormal external access attempt is detected, operators must promptly report it to financial authorities in a manner similar to financial companies.
The FSC will also ease regulations so exchanges can pre-emptively block deposits and withdrawals even before hacking is clearly confirmed.
The current Digital Asset User Protection Act prohibits blocking deposits and withdrawals without a justifiable reason and allows blocks only when a hacking incident is clearly evident.
As a result, the industry has raised concerns that it is unclear whether deposits and withdrawals can be blocked at an early stage when hacking is suspected, such as unusual transactions.
The FSC said rapid blocking in the early stage of an incident, as in the Binance hacking case, is important to prevent the spread of damage. It will issue a "non-action letter" under which it will not sanction operators even if they pre-emptively block deposits and withdrawals when hacking or a security breach is suspected.
It will also expand security support through the Financial Security Institute. Of the 28 digital asset operators, only 5 won-market exchanges are currently members of the institute.
The FSC plans to push for additional membership by other operators and to provide threat information sharing, checks for security vulnerabilities and professional financial security training. For operators that find it difficult to join, it will support vulnerability factor searches and alerts and security measures at the level of small and mid-sized financial companies.
The institute will also establish security inspection standards tailored to digital asset exchanges. It plans to improve existing inspection standards by year-end to reflect stronger transaction verification and wallet access controls.
 Sangyeop Oh
yub@d-today.co.kr