
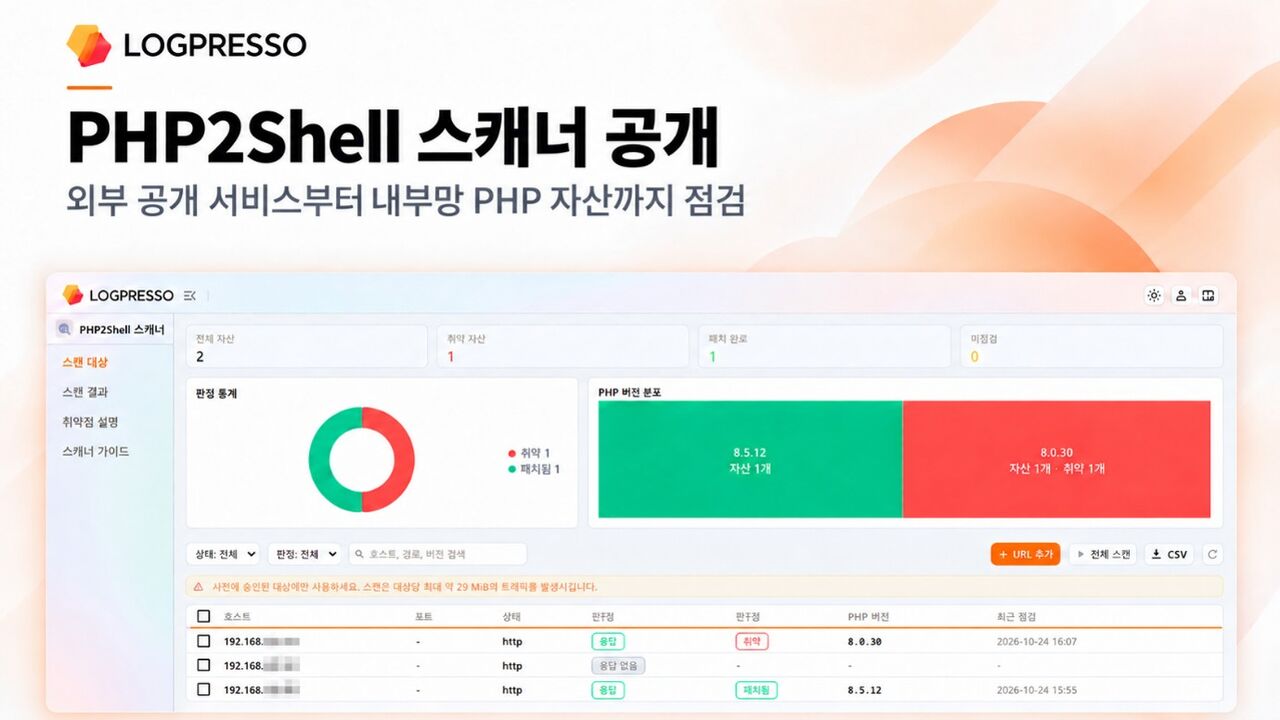
Logpresso, an integrated security company, said on Oct. 26 it has released a "PHP2Shell Scanner" app on the Logpresso Store for customers to diagnose the PHP remote code execution vulnerability "PHP2Shell".
The vulnerability is not in a specific application but a flaw in the PHP engine, so all web services that run on PHP are subject to checks.
Logpresso also posted a response advisory on its blog on Oct. 21 that includes how to identify vulnerable PHP assets, temporary mitigation measures and how to check for signs of compromise. It also released the PHP2Shell Scanner.
Users can run a diagnosis immediately by installing the app on Logpresso SIEM-XDR and registering the URL to be checked.
The PHP2Shell Scanner also checks internal network PHP assets that can be accessed from the Logpresso server. Users can register multiple target URLs in bulk, and it automatically determines whether to connect via HTTP or HTTPS. It records whether each asset is vulnerable and the PHP version information identified during diagnosis, and provides decision statistics on vulnerability status and an asset distribution by PHP version.
After applying a patch, users can recheck the registered targets with a single button.
Yang Bong-yeol (양봉열), Logpresso's chief executive, said, "Following the response advisory, we have released the scanner so that customers can check their assets directly." He added, "We will support customers so they can check internal network PHP assets within their existing security operations environment and continue to confirm the results of actions taken after patching."
 Chi-gyu Hwang
delight@d-today.co.kr