
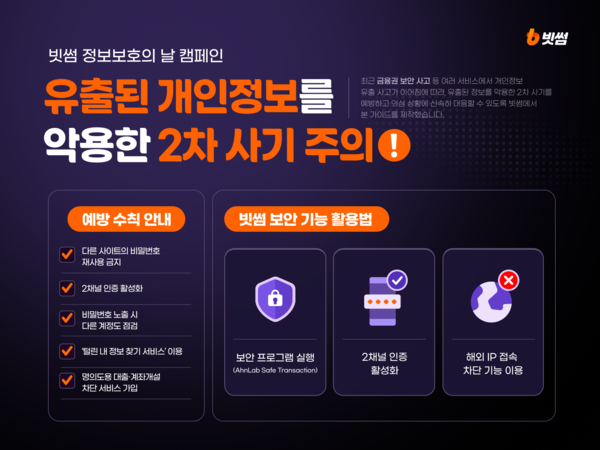
Bithumb is moving to prevent 피해 from secondary cybercrime such as phishing and voice phishing that exploits personal data leaks.
Bithumb said on Thursday it will run a campaign to prevent 피해 from “secondary scams exploiting leaked personal information” as part of its October information security campaign.
It comes as personal data leaks continue across the financial sector and other services, leading to an increase in tailored crimes that use already leaked information to approach victims.
Fraudsters approach victims using phrases such as, “Your information has been leaked and you are eligible for compensation,” and “We need to verify your account for a security inspection.”
They present not only names, mobile phone numbers and email addresses but also past order numbers, service names used, and parts of previous passwords to gain trust. They then诱導 victims to visit phishing sites, install remote-control apps or transfer funds.
During this process, identity verification information, IDs, account information and authentication codes can be further leaked. There is also a possibility it leads to financial losses, such as by repeatedly entering obtained passwords into other services to hijack accounts or by demanding upfront payments under the pretext of loan refinancing.
Bithumb stressed that the fact that someone knows a person’s personal information cannot itself serve as grounds that the contact is from an official agency or a financial company.
It recommended that even if users receive texts, emails or messenger messages citing identity theft, compensation for 피해 or security checks, they should not use the included links. It said they should instead access the official app or website they normally use directly to verify.
It also urged users to strengthen password management. It said users should not reuse passwords used on other sites or issued temporarily, and should set a separate password used only on Bithumb. If a password leak is suspected, users should also change other services that use the same or similar passwords.
It also 안내ed a method to check whether IDs and passwords are being illegally distributed by using the “Find My Leaked Information” service operated by the Personal Information Protection Commission and the Korea Internet & Security Agency.
Security features provided by Bithumb include “two-channel authentication” and “blocking overseas IP access.” Two-channel authentication requires additional authentication after entering an ID and password.
It also provides AhnLab Safe Transaction, which supports keyboard input protection, phishing blocking and memory hacking prevention.
If an alert arrives about a change to security settings, users should immediately 확인 whether they made the change themselves. If identity theft is a concern, users can use the financial transaction reassurance blocking service or the Financial Supervisory Service’s “Fine” personal information exposure accident prevention system to restrict unauthorized credit transactions and non-face-to-face account openings.
If users have already entered personal information or executed a suspicious installation file, they should immediately cut network connections. They should then take account-protection measures on a separate, uninfected device, including changing their Bithumb password, resetting two-factor authentication, deleting API keys and checking the withdrawal address whitelist.
A Bithumb official said, “Once personal information is leaked, it can continue to be exploited.” The official added, “We will continuously strengthen security and expand preventive campaigns.”
 Oh Sang-yup
yub@d-today.co.kr