
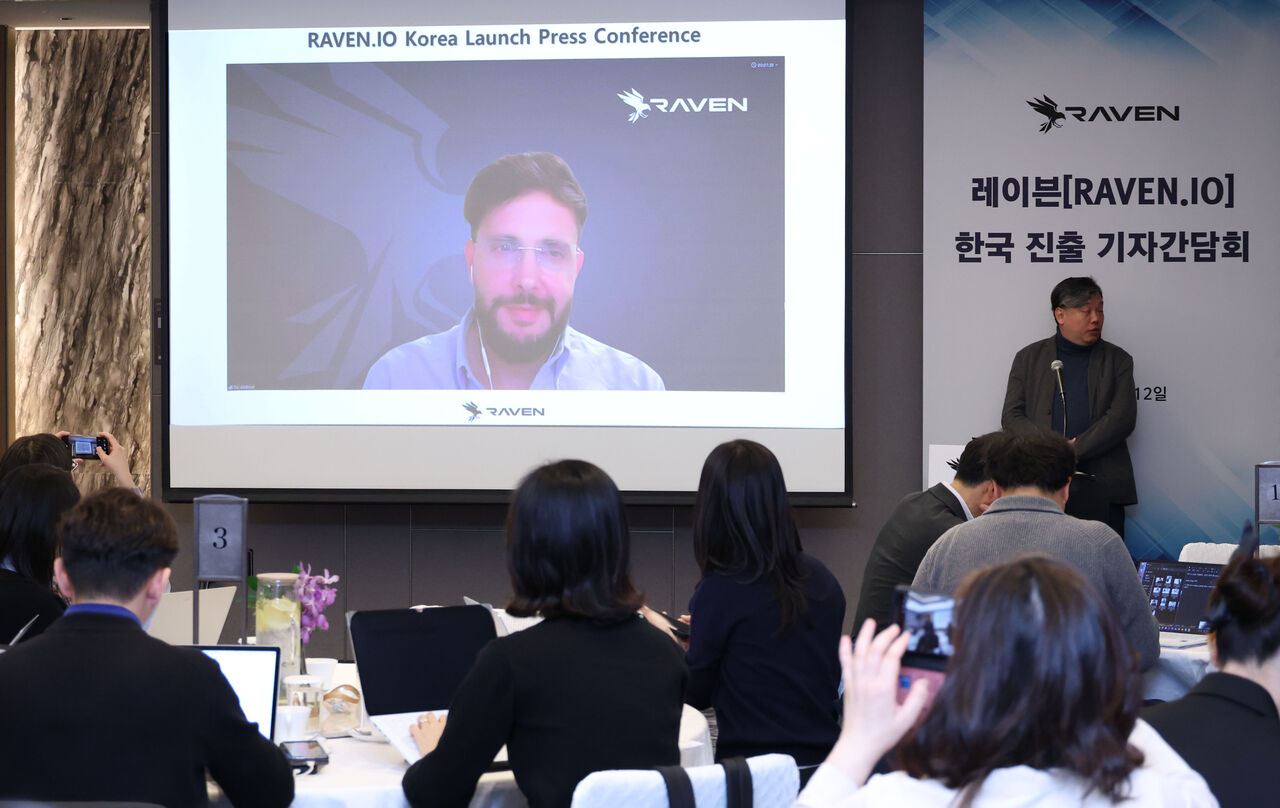
Raven, a global runtime application security company, held a press briefing on Wednesday and officially announced its entry into the South Korean market.
At the briefing, Raven introduced its business strategy for South Korea and its approach to application protection. It said it will provide technology to protect corporate assets and information from AI-based vulnerability exploitation attacks that have recently emerged as an issue.
Raven.io plans to target heavily regulated industries, including finance, first through a partnership with Singapore-based business consulting and services company The Executive Action.
It plans to focus its business on organisations that consider protecting sensitive data, maintaining operational resilience and securing complex application environments as key business tasks.
The company said its Raven solution monitors how open-source components operate at runtime and provides visibility into libraries, functions and execution paths inside running applications. Its runtime attack prevention function is designed to identify and block abnormal execution without relying only on published Common Vulnerabilities and Exposures (CVE) records or known vulnerability exploitation signatures.
This approach supports companies in going beyond identifying a list of installed components to understanding how trusted code actually behaves at runtime. For example, a library that decodes data should not need to execute external commands. Identifying such unexpected behaviour can allow intervention when an attacker tries to exploit a legitimate component as an intrusion path.
Roy Avitbul (로이 아비트불), Raven co-founder and chief executive officer, said companies cannot rely on an approach that starts protection only after a CVE is disclosed. "Attackers can also analyse the same open-source code that companies use," he said. "Security teams must understand what that code does at runtime and be able to block vulnerability exploitation even when there are no known vulnerabilities or attack signatures."
 Chi-gyu Hwang
delight@d-today.co.kr