
Search results for CVE
AI & Enterprise
Piolink finds 28 previously unknown open-source vulnerabilities using BlueHunter
Piolink said on Wednesday it found 28 previously unknown new vulnerabilities in open-source software using its self-developed CTEM-based cyber threat management platform, BlueHunter. Two of the cases have been assigned CVE identifiers, and related information is scheduled to be officially disclosed in December. Piolink said its Threat Analysis Center analyzed the attack surface and software behavior of 10 open-source services and 1 CMS used in Linux environments.
Industry
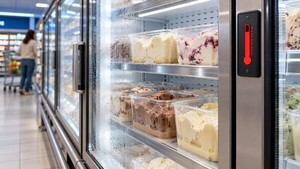
Hack forces fridge temperatures up to 50C at hundreds of French supermarkets
Hundreds of large supermarkets in France were hit by a cyberattack that caused refrigeration and freezing equipment to malfunction, expanding losses as hackers remotely altered fridge temperatures. The attack, reported to have occurred between the night of Oct. 11 and Oct. 12, targeted temperature management systems. Affected companies included E. Leclerc, Intermarche and Cooperative U. Some stores saw settings rise to 50 degrees Celsius, forcing disposal of chilled and frozen food.
Telecommunications & Media
Apple issues emergency security patch for iPhone and Mac users on iOS 26
Apple has fixed a security vulnerability found in iOS 26, iPadOS 26 and macOS 26, saying the flaw may already have been exploited and could have been used in highly sophisticated attacks targeting users on versions before iOS 27. The weakness was found in a core graphics engine used for interface and screen processing. Apple classified it as CVE-2026-86950. Meta’s security team discovered the flaw.
-
AI & Enterprise
AI hacking undermines OT security-through-obscurity strategy
-
AI & Enterprise
CrowdStrike report flags vulnerability exploitation concentrated within 48 hours
-
AI & Enterprise
Ruby on Rails patches critical CVSS 9.5 flaw, urges update
-

AI & Enterprise
JSecurity launches domain-based attack surface management, dark web data leak detection solution in Korea
-

AI & Enterprise
Ransomware targeting AI models emerges, encrypting training weights and raising recovery cost concerns
-

AI & Enterprise
Cl0p ransomware affiliate shows signs of exploiting PTC Windchill, FlexPLM flaw
-
AI & Enterprise
No time to respond to ultra-fast AI attacks, \'patch gap\' alarm
-
AI & Enterprise
Rise of zero trust, zero CVE security requires zero ops strategy
-
Games & Commerce
18-year-old Excel bug still used in attacks, warning for legacy Office users
-
AI & Enterprise
Tech Insight: Why software supply chains are being breached quickly amid the spread of AI coding
-
AI & Enterprise
VMware Aria Operations flaw exploited in real-world attacks