
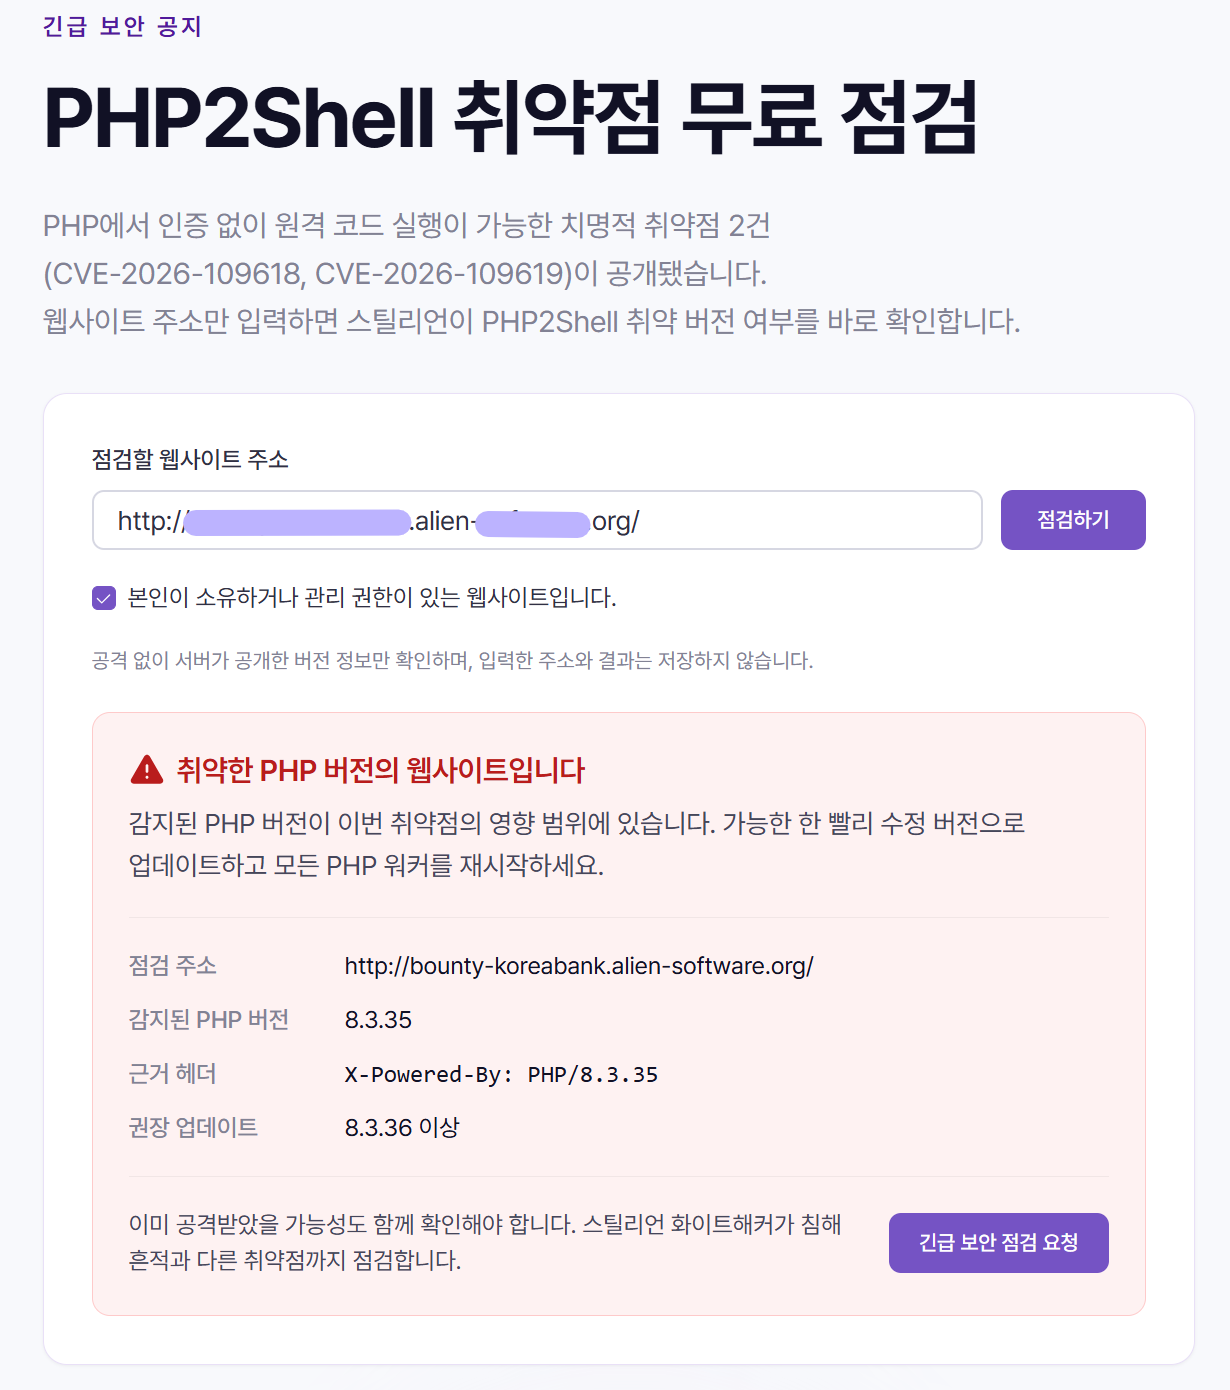
Stealien, an AI security company, said on Wednesday it has launched a free online service that checks whether a website is affected by the PHP2Shell vulnerability by entering a website address (URL).
Users can access a dedicated page on Stealien's website (stealien.com/php2shell) and enter the address of a website to check whether it is vulnerable. The results are provided within the scope of confirming the vulnerability and do not guarantee overall website safety or replace security updates.
PHP2Shell is a collective term for two major security vulnerabilities found in PHP, which is widely used to run web services (CVE-2026-109618, CVE-2026-109619). If exploited, an unauthenticated attacker can execute arbitrary code on a server or access sensitive information.
PHP is used for various web services such as homepages, online shopping malls, message boards and admin pages. Website-building tools widely used in South Korea, including WordPress and Gnuboard, also run on PHP. The latest vulnerabilities are an issue with PHP itself rather than individual website code, meaning a website can be affected even if it was developed securely if it uses a vulnerable PHP environment.
Stealien also stressed that, separately from the online check results, users should confirm whether PHP security updates have been applied and whether related web services have been restarted after the update.
Park Chan-am (박찬암), Stealien's chief executive, said that in urgent situations like this it is important to check whether a running service is affected and take swift security measures. He said the company released the service in hopes it will help small and medium-sized companies and institutions that lack security personnel.
 Chi-gyu Hwang
delight@d-today.co.kr