
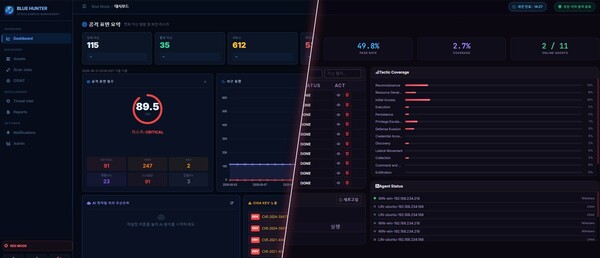
Piolink said on Oct. 15 it found 28 previously unknown new vulnerabilities in open-source software by using its self-developed CTEM-based cyber threat management platform, BlueHunter.
Two of the cases have been assigned CVE (Common Vulnerabilities and Exposures) identifiers. Related information is scheduled to be officially disclosed in December.
According to the company, Piolink's Threat Analysis Center, which developed BlueHunter, analyzed the attack surface and software behavior of 10 open-source services and 1 content management system used in Linux environments. It found new vulnerabilities that could cause memory access errors and abnormal termination. It also confirmed that some vulnerabilities could have an impact not only when executing specific commands but also during Linux system device recognition and management processes.
The company stressed that the result is meaningful because it went beyond general security checks that detect previously disclosed vulnerabilities. It said it used BlueHunter to directly discover and verify new security vulnerabilities.
The Threat Analysis Center built a reproducible environment for each vulnerability it found and reported them to the official maintainers of the relevant open-source projects after repeated verification. The two sides are conducting a technical review of the scope of the impact and ways to fix the vulnerabilities.
Piolink CEO Young-cheol Cho (조영철) said, "As AI-enabled attacks are spreading rapidly, defense must also evolve toward finding potential vulnerabilities before attackers do." He added, "We will continue to proactively discover potential security threats based on BlueHunter and strengthen software supply chain security by contributing to vulnerability verification and fixes in cooperation with open-source development projects."
 Chi-gyu Hwang
delight@d-today.co.kr