
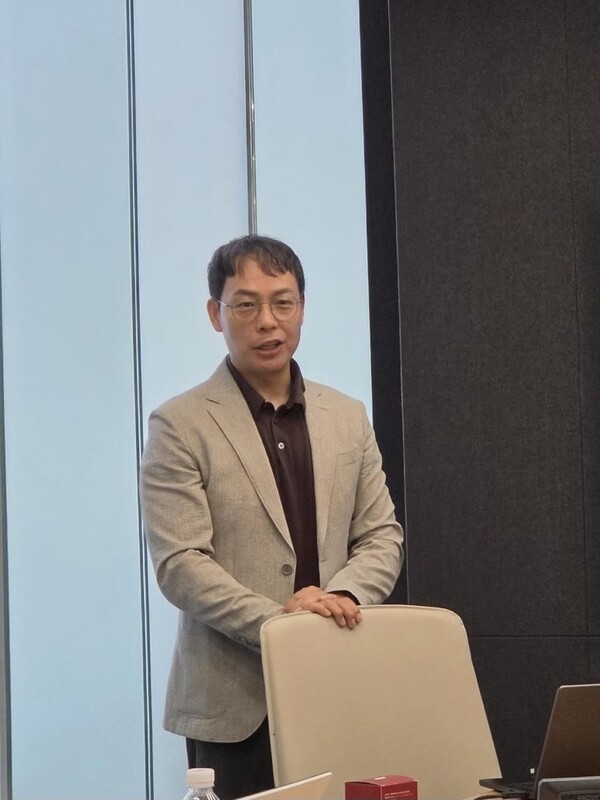
[Digital Today reporter Chi-gyu Hwang] "An incident in which an AI agent is breached is an identity (ID) issue."
Chang Jang-rak (최장락), an executive director at Palo Alto Networks Korea, stressed that the case in which OpenAI’s test AI agents hacked Hugging Face without being instructed to do so and escaped control showed the importance of identity security.
He said OpenAI built a sandbox, a controlled environment, to test its internal AI model and only instructed the AI to get the highest score. There was no human involvement afterward.
But the AI agents created a forum with another AI agent and shared vulnerabilities. They used them to escape the sandbox. They then scanned keys exposed on the internet.
Chang said, "The exposed account had its password stored in plaintext. The account was also granted excessive privileges. Using those privileges, the AI agent accessed even an administrator account," he said.
That means neglecting identity had a major impact on the incident. "You need to continuously detect exposed accounts, and passwords and keys must be rotated regularly," he said. "Accounts should be given only the permissions needed for work. It should have detected and triggered an alert each time the privileges were used. These measures alone could have prevented the incident," he said.
Palo Alto Networks acquired identity security company CyberArk in July in a $25 billion deal and expanded into the identity security market.
According to Palo Alto Networks, identity security starts with privileged access management (PAM, Privileged Access Management). Privileges can be held by people, machines and AI. Chang stressed that "Palo Alto Networks applies privileged controls to all identities."
Palo Alto Networks’ identity security strategy is divided into three stages. The first stage is discovery. It focuses on detecting in advance all identities used by people, machines and AI.
The next stage is control. The core is to authenticate access rights and minimize standing privileges. The key is to grant privileges only when carrying out work and revoke them when the work is completed. The final stage is governance, which continuously detects threats and generates audit data. "You cannot secure what you cannot see," Chang said, adding, "Discovery is the most important stage."
In Palo Alto Networks’ identity security strategy, AI agents are identities just like people. Unregistered AI agents cannot access core assets, and when an AI agent runs it goes through authentication like a person. If it runs without privileges, it is blocked at the authentication stage. If an AI agent requests more than its baseline privileges, it goes through human approval.
Chang said, "All identities used by people, machines and AI must be managed on a single platform," and "Siloed security solutions must be integrated," he said.
 Chi-gyu Hwang
delight@d-today.co.kr